



What's Happening?
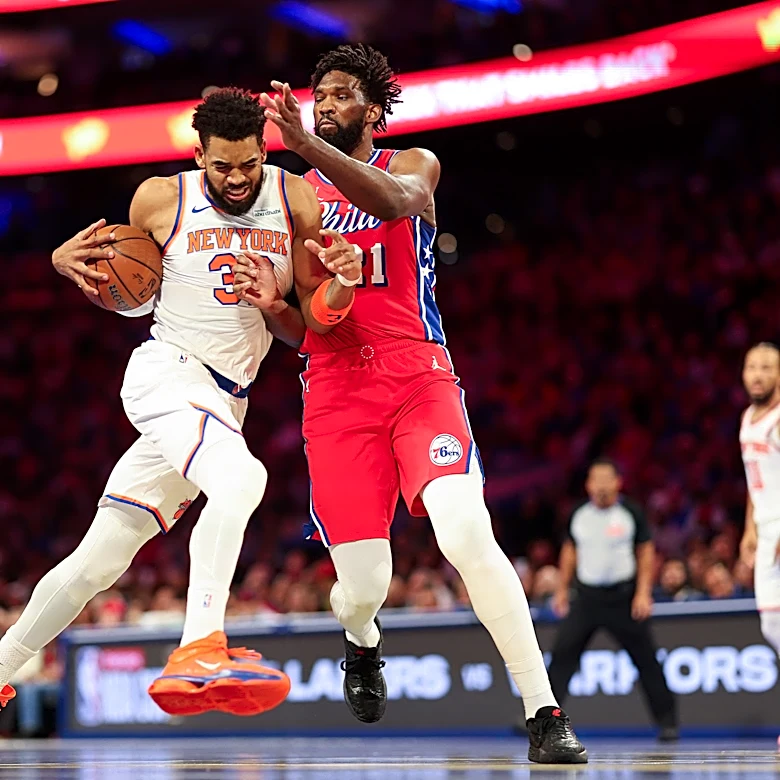
The New York Knicks organization has admitted to an "unfortunate mistake" after conducting a cybersecurity phishing test that lured employees with the promise of free championship rings. Employees received an email offering personalized rings, purportedly
from the same company that crafts rings for players. Those who clicked on the link in the email, which directed them to a page to choose ring designs, were subsequently enrolled in mandatory cybersecurity training. This test followed a previous incident where a deceptive email successfully tricked employees into divulging login credentials, leading to unauthorized access to company systems and an extortion attempt. Madison Square Garden Sports stated that this prior breach prompted a stronger focus on staff awareness regarding cybersecurity threats. The organization acknowledged that using the expectation of championship rings as bait was inappropriate.
Why It's Important?
This incident highlights the growing challenge organizations face in balancing cybersecurity vigilance with employee morale and trust. While the intent was to bolster security awareness after a real data breach, the method employed by the Knicks could erode employee trust and foster resentment. Employees, who already anticipated receiving championship memorabilia, felt misled by the organization. This approach risks creating a cynical workforce less likely to engage positively with future security initiatives. For businesses, it underscores the importance of designing cybersecurity training and phishing simulations that are effective without being deceptive or damaging to internal relationships. The incident also brings to light the broader issue of how companies communicate and manage expectations around employee rewards and recognition, especially in high-profile sports organizations where such gestures carry significant symbolic weight.
What's Next?
The New York Knicks organization has issued an apology, acknowledging the mistake in their approach. Moving forward, they will likely need to re-evaluate their cybersecurity training strategies to ensure they are both effective and respectful of their employees. This may involve implementing more transparent and less deceptive methods for testing security awareness. The organization also plans to distribute over 275 pieces of commemorative jewelry to players, coaches, and staff, worth more than $3.7 million, though details on who will receive actual rings versus other jewelry remain unclear. The incident may prompt other companies to review their own cybersecurity testing protocols to avoid similar pitfalls and maintain positive employee relations while strengthening their digital defenses.
Beyond the Headlines
The Knicks' phishing test raises ethical questions about the boundaries of corporate security measures and employee manipulation. While companies have a legitimate need to protect their digital assets, using highly anticipated rewards as bait can be seen as a breach of trust. This incident could lead to a broader discussion within the corporate world about the psychological impact of such tests and whether the benefits of enhanced security outweigh the potential damage to employee morale and loyalty. It also underscores the evolving nature of cyber threats, where human error remains a significant vulnerability, and the complex challenge of educating employees without resorting to tactics that feel punitive or deceptive. The incident serves as a case study for how not to conduct internal security awareness campaigns, emphasizing the need for empathy and clear communication in cybersecurity education.