


What's Happening?
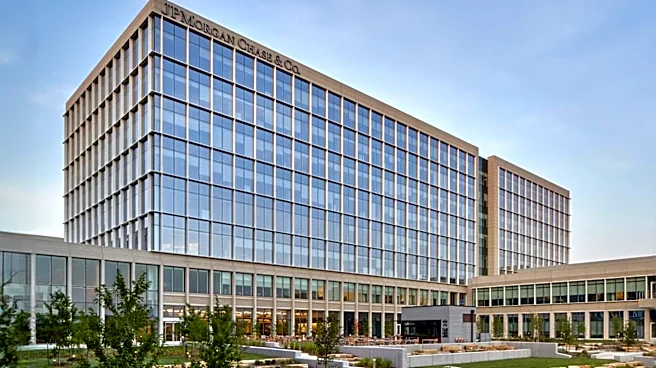
JPMorgan Chase has confirmed that certain customer marketing data, including names and email addresses, may have been accessed in a cyberattack targeting third-party service providers. The bank stated that its services remain operational and that the
incident is unrelated to recent transaction processing delays experienced by some customers. While the cyber extortion group n0n claimed responsibility for leaking information associated with JPMorgan Chase, Visa, and Mastercard, the bank's investigation indicates that the breach primarily affected marketing data held by external vendors. JPMorgan Chase plans to contact affected customers and offer support, including complimentary credit monitoring. The incident highlights the vulnerabilities that can arise when financial institutions rely on outside service providers for data handling.
Why It's Important?
This cyberattack on third-party vendors impacting JPMorgan Chase underscores a significant and growing risk within the U.S. financial sector. The reliance on external service providers, while often efficient, introduces additional points of vulnerability that can be exploited by cybercriminals. Even if core banking systems remain secure, the exposure of marketing data like names and email addresses can lead to increased phishing attempts and social engineering scams. This incident could erode customer trust in financial institutions' ability to protect their personal information, even when the breach occurs outside the bank's direct control. For consumers, the immediate concern is the potential for more sophisticated and targeted scams, requiring heightened vigilance against fraudulent communications. For the financial industry, it emphasizes the critical need for robust cybersecurity protocols and rigorous vetting of all third-party vendors that handle sensitive customer data.
What's Next?
JPMorgan Chase intends to contact affected customers and provide complimentary credit monitoring, a standard response to data breaches. Customers should anticipate an increase in phishing emails and other scam attempts that leverage the exposed marketing data to appear more legitimate. The financial industry, including JPMorgan Chase, will likely face increased scrutiny regarding their third-party vendor management and cybersecurity practices. Regulators may push for stricter guidelines on data sharing and security requirements for external service providers. Individuals are advised to strengthen their online security by using unique passwords, enabling multi-factor authentication, and monitoring their bank accounts for suspicious activity. The full extent of the breach and the identity of all affected vendors are still under investigation, suggesting that more details and potential impacts could emerge.
Beyond the Headlines
This incident extends beyond a typical data breach, highlighting the complex and interconnected nature of modern data ecosystems. The fact that a cyberattack on third-party vendors can compromise customer data from major financial institutions like JPMorgan Chase reveals a systemic vulnerability. It raises ethical questions about the extent to which customers are informed about, and can consent to, their data being handled by numerous external entities. The long-term implications could include a re-evaluation of data privacy regulations, potentially leading to stricter accountability for financial institutions regarding their vendors' security practices. Furthermore, it could accelerate the adoption of advanced security measures, such as zero-trust architectures, across the financial sector to mitigate risks associated with third-party access. The incident also underscores the ongoing challenge of balancing convenience and data security in an increasingly digital world.