
What's Happening?
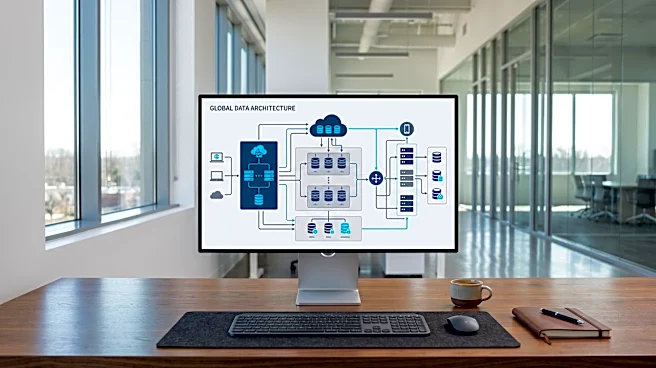
Splunk is providing guidance on how to create comprehensive Security Information and Event Management (SIEM) architecture diagrams. This initiative aims to help organizations map their log sources and pipelines effectively. The process involves exporting
log sources from Splunk, along with an asset list, and then using a tool like Eraser to generate a visual diagram. This diagram illustrates which systems are sending logs, how these logs are collected, and which systems are not sending any logs, highlighting potential coverage gaps. The methodology emphasizes the importance of a clear understanding of data flow from source systems through the collection tier to the SIEM and its output consumers. Splunk's approach leverages existing `metadata` and `tstats` commands to extract relevant information, which is then shaped into structured CSV files for diagram generation. The guide also details how to represent the collection tier, including universal forwarders, syslog collectors, and HTTP Event Collectors (HEC), ensuring that every log path is clearly defined and traceable.
Why It's Important?
This guidance is crucial for U.S. businesses and government agencies that rely on SIEM systems for cybersecurity and operational monitoring. By providing a structured method for visualizing SIEM architecture, Splunk helps organizations identify and address critical blind spots in their logging infrastructure. Unidentified gaps in log collection can leave systems vulnerable to cyber threats, as security teams may lack the necessary data to detect and respond to incidents. The ability to clearly map log sources and collectors enhances an organization's security posture, improves compliance with regulatory requirements, and optimizes the performance and availability of their logging platforms. Furthermore, this detailed architectural understanding can streamline troubleshooting processes and facilitate more efficient audits, ultimately safeguarding sensitive data and critical operations across various sectors, including federal agencies and enterprises with complex IT environments.
What's Next?
Organizations are encouraged to adopt these practices to regularly review and update their SIEM architecture diagrams. The process involves exporting current log source data and asset lists, generating updated diagrams, and verifying them against their operational reality. This continuous monitoring and updating will ensure that the diagrams accurately reflect the evolving IT landscape and security needs. Future developments may include further integration of such diagramming capabilities directly within SIEM platforms or enhanced AI-driven tools to automate the identification of logging gaps and suggest remediation actions. The emphasis will likely remain on proactive security measures and maintaining a clear, verifiable understanding of data flows to counter increasingly sophisticated cyber threats.
Beyond the Headlines
The push for detailed SIEM architecture diagrams reflects a broader industry trend towards greater transparency and accountability in cybersecurity. Beyond mere technical implementation, this initiative touches upon the ethical responsibility of organizations to protect data and maintain operational integrity. The ability to visualize and audit log sources can foster a culture of security awareness, where every system owner understands their role in contributing to the overall security posture. Legally, such detailed documentation can be vital in demonstrating due diligence during incident response or regulatory compliance audits. Culturally, it promotes a shift from reactive problem-solving to proactive risk management, encouraging a more holistic and integrated approach to cybersecurity across an organization.