


What's Happening?
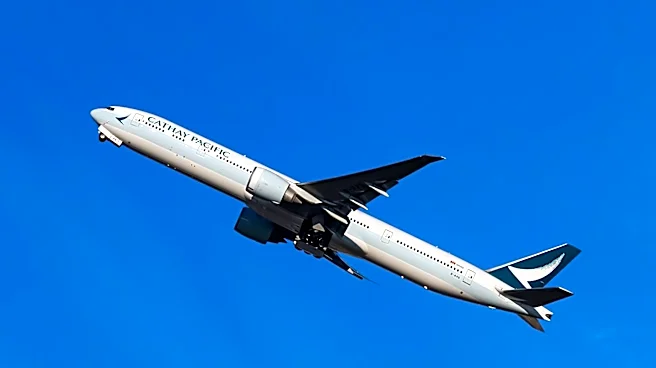
Cathay Pacific has confirmed that approximately 53,000 of its bookings were affected by unauthorized access to one of Amadeus's systems. The breach occurred between August 2023 and September 2026. Amadeus, a global travel technology provider serving over
400 airlines, has taken steps to contain the incident, including a password reset, and has implemented enhanced monitoring and detection capabilities. While Amadeus has not yet identified evidence that the affected data has been misused, the incident has prompted concerns about supply chain security within the airline industry. Other airlines, including Qantas, Korean Air, Asiana, Japan Airlines, ANA, and Malaysia Airlines, were also impacted by the breach.
Why It's Important?
This cyber attack highlights the significant cybersecurity risks inherent in the interconnected global travel industry. The reliance of numerous airlines on third-party technology providers like Amadeus means that a breach in one system can have widespread implications across multiple carriers and potentially compromise sensitive customer data. For Cathay Pacific, the incident affects a substantial number of bookings, raising questions about customer trust and data privacy. The lack of identified misuse of data so far is a positive, but the potential for future exploitation remains a concern. This event underscores the critical need for robust cybersecurity measures and vigilant oversight of third-party vendors to protect consumer information and maintain operational integrity.
What's Next?
Amadeus has already implemented a password reset and enhanced monitoring capabilities to mitigate further risks. Cathay Pacific and other affected airlines will likely continue to work with Amadeus to fully understand the impact on their bookings and customers. It is probable that these airlines will communicate directly with affected customers regarding the breach and any necessary actions, such as password changes or monitoring for suspicious activity. The incident may also prompt a broader review of cybersecurity protocols and supply chain security within the airline industry, potentially leading to stricter requirements for third-party vendors and increased investment in data protection technologies.
Beyond the Headlines
The Amadeus cyber attack brings to light the complex ethical and legal responsibilities of companies handling vast amounts of personal data. While Amadeus claims no evidence of data misuse, the unauthorized access itself constitutes a breach of trust. This incident could lead to increased regulatory scrutiny on data security practices in the travel sector, potentially resulting in new compliance mandates and penalties for companies that fail to adequately protect customer information. Furthermore, it emphasizes the growing importance of 'supply chain security' in the digital age, where the weakest link in a network can expose an entire ecosystem to risk. This event serves as a stark reminder that cybersecurity is not just an IT issue, but a fundamental business and ethical imperative.