

What's Happening?
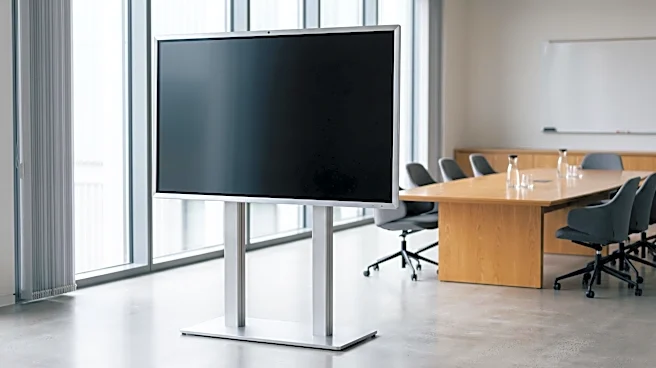
Interactive boards, such as those used in Teams Rooms devices and other smart board applications, should ideally be placed on their own isolated network segment. This recommendation comes from Microsoft for its Teams Rooms devices and is advised for other interactive
boards as well. The primary goal is to prevent display traffic from interacting with sensitive systems like finance and human resources. Beyond network segmentation, securing these devices involves several critical steps: updating to the latest firmware, changing default passwords, disabling unused services, and enrolling them in a management tool. The operating system, whether Android or Windows, is less critical than consistent patching, proper configuration, and active management. Vulnerabilities have been identified in various interactive display components, including unauthenticated flaws in sharing services and insecure default configurations, underscoring the need for robust security practices.
Why It's Important?
The security of interactive boards is crucial for U.S. businesses and educational institutions, as these devices often handle confidential information and are connected to broader organizational networks. A compromised interactive board could serve as an entry point for cyberattacks, potentially leading to data breaches, system disruptions, and significant financial and reputational damage. By isolating these devices on separate network segments, organizations can create a barrier that limits the potential impact of a security incident. Furthermore, neglecting basic security measures like firmware updates and password changes leaves organizations vulnerable to known exploits, making them easy targets for malicious actors. The emphasis on management tools highlights the need for proactive IT strategies to maintain a secure digital environment, protecting sensitive data and ensuring operational continuity.
What's Next?
Organizations deploying or currently using interactive boards should prioritize a comprehensive security audit of their existing infrastructure. This includes verifying that all interactive displays are on isolated network segments, that default passwords have been changed, and that all unnecessary services are disabled. IT departments should establish a regular schedule for firmware updates and ensure that all devices are enrolled in a centralized management tool for consistent oversight. Furthermore, ongoing training for users on secure practices, such as signing out and clearing content after each session, will be essential. Vendors of interactive displays are expected to continue improving the security features of their products, but the ultimate responsibility for implementation and maintenance lies with the end-user organizations.
Beyond the Headlines
The increasing integration of interactive displays into corporate and educational environments highlights a broader trend of expanding attack surfaces in modern digital ecosystems. As more devices become interconnected, the importance of a 'zero-trust' security model, where no device or user is inherently trusted, becomes paramount. The vulnerabilities in interactive boards underscore the need for a holistic security approach that extends beyond traditional endpoints to include all networked devices. This situation also raises ethical considerations regarding data privacy, especially when interactive boards are used in public or shared spaces where sensitive information might be displayed or stored. Organizations must balance the benefits of collaborative technology with the imperative to protect data and maintain privacy, potentially influencing future regulatory frameworks for connected devices in shared environments.