

What's Happening?
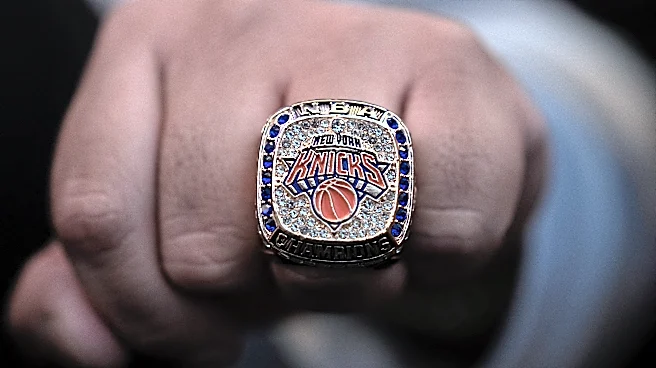
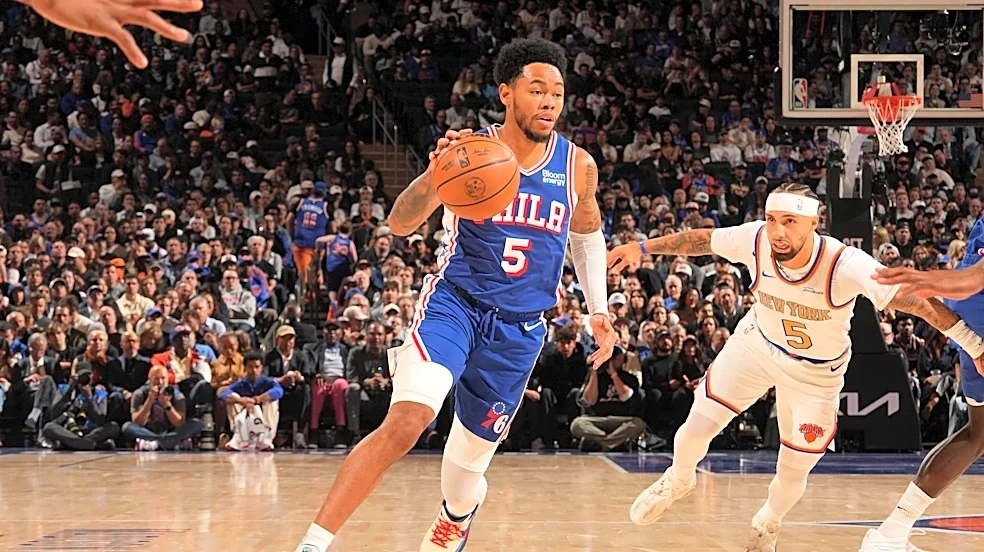
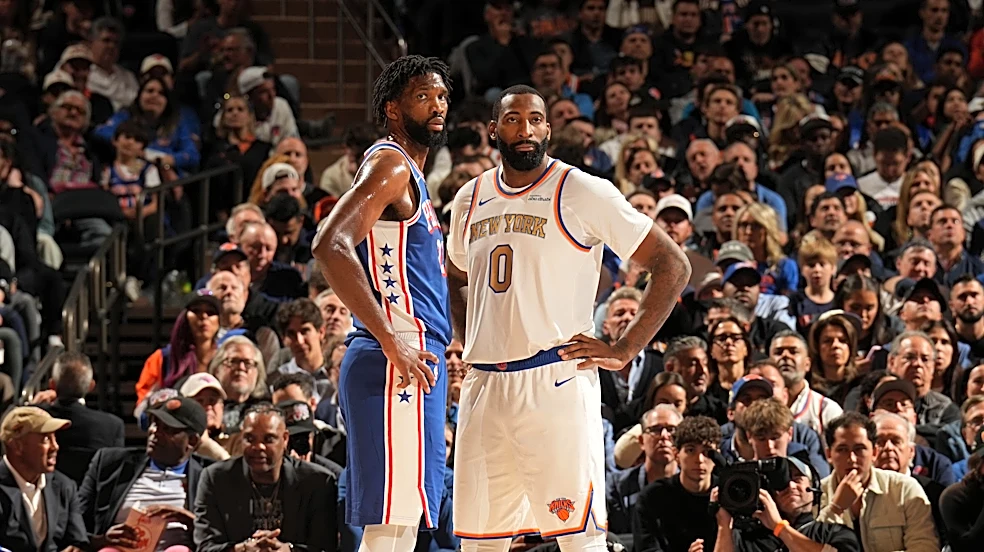
Madison Square Garden (MSG) conducted a cybersecurity phishing test by sending employees a fake email promising Knicks NBA championship rings. Employees who clicked the fraudulent link were then required to take a cybersecurity class. This incident, reported
by The Athletic, occurred despite the company's spokesperson later stating that over 275 actual championship rings and jewelry would be gifted to players, coaches, employees, and other members of the Knicks family. The spokesperson described the use of the rings in the phishing email as 'an unfortunate mistake.' The event has brought to light the contentious nature of phishing simulations as a cybersecurity measure.
Why It's Important?
This incident at Madison Square Garden highlights a significant debate within corporate cybersecurity practices regarding the efficacy and ethical implications of phishing simulations. While intended to bolster security, such tests can erode employee trust and foster resentment, particularly when they exploit emotionally resonant incentives like championship rings. For U.S. businesses, this raises questions about the balance between security measures and employee morale. Critics argue that these exercises do not accurately simulate real-world threats and can lead to inaction when genuine threats emerge. The potential for negative side effects, such as decreased trust in management and a cynical view of cybersecurity training, could ultimately undermine the very security culture companies aim to build. This event serves as a case study for other organizations considering similar tactics, emphasizing the need for careful consideration of psychological impacts on their workforce.
What's Next?
Following the backlash and public discussion surrounding MSG's phishing test, other companies may re-evaluate their cybersecurity training methodologies. There could be a shift towards more transparent and less deceptive approaches to employee cybersecurity education. Organizations might explore alternative training methods that focus on building genuine awareness and critical thinking skills without resorting to trickery. Furthermore, the incident could prompt a broader discussion within the cybersecurity industry about best practices for employee engagement and the ethical boundaries of security testing. Companies might invest in more sophisticated, non-deceptive tools or programs that simulate threats in a way that educates rather than alienates employees, potentially leading to new industry standards for cybersecurity training.
Beyond the Headlines
The MSG phishing incident touches upon deeper implications concerning corporate culture, employee trust, and the evolving nature of workplace security. Ethically, the use of a highly desirable, yet fake, reward to test employees raises questions about manipulation and the psychological contract between employer and employee. It underscores a potential disconnect between management's security objectives and the human element of the workforce. Culturally, such tactics can foster an environment of suspicion rather than collaboration, potentially impacting overall productivity and employee loyalty. Legally, while phishing tests are generally permissible, repeated or overly deceptive practices could theoretically lead to grievances or challenges regarding workplace conduct. This event highlights the critical need for organizations to consider the human impact of their security strategies, recognizing that effective cybersecurity is not just about technology, but also about fostering a culture of trust and genuine understanding among employees.