

What's Happening?
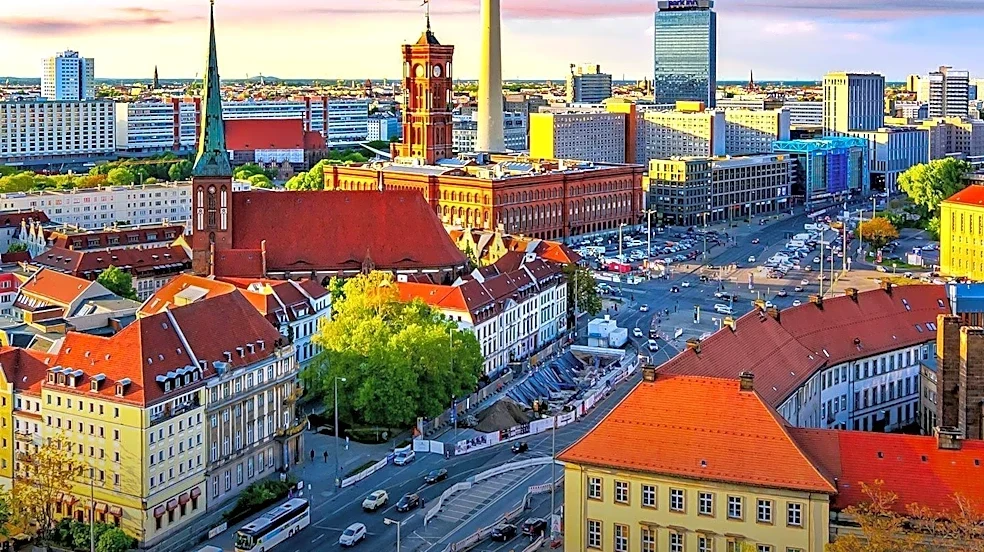
Germany is increasingly focusing on sovereign compliance frameworks, such as C5, which blends elements of SOC 2, ISO, and NIST standards. This emphasis is part of a broader global trend where countries are developing their own specific security and compliance requirements
for businesses operating within their borders. For companies looking to enter or expand into the German market, particularly in sectors like automotive, adherence to these localized frameworks is crucial. The recommended strategy for businesses is to establish a unified control set, often based on foundational frameworks like ISO 27001 and NIST 800-53, and then identify and address specific gaps to meet individual sovereign compliance demands. This approach aims to streamline the compliance process, making it more efficient for organizations to adapt to various international standards without repeatedly building new frameworks from scratch. The discussion highlights that while these frameworks may appear diverse, many share common underlying principles, simplifying the process of achieving compliance across multiple jurisdictions.
Why It's Important?
The growing demand for sovereign compliance, as exemplified by Germany's C5 framework, significantly impacts U.S. businesses seeking global expansion. It necessitates a strategic shift from a singular compliance focus to a more integrated, cross-functional approach involving CISOs, product leaders, and chief revenue officers. Without a unified strategy, U.S. companies risk missteps in market entry, potentially leading to delays or missed opportunities. The ability to efficiently map existing controls (like ISO 27001) to new sovereign requirements can provide a competitive advantage, reducing the time and resources needed for compliance. Conversely, companies that fail to adapt to these evolving international standards may find themselves locked out of lucrative markets, impacting their global revenue streams and overall competitiveness. This trend underscores the increasing complexity of international business operations and the critical role of robust compliance frameworks in facilitating global trade and market access.
What's Next?
U.S. businesses aiming for global expansion, particularly into markets with stringent sovereign compliance requirements like Germany, will need to prioritize the development of cross-functional working groups. These groups, comprising sales, GRC, CISO, and product teams, will be essential for aligning internal strategies with external compliance demands. The focus will be on conducting structured mapping exercises to identify and address incremental gaps between existing security controls and new sovereign standards. This proactive approach will enable companies to anticipate and meet compliance obligations more effectively, preventing potential market entry hurdles. Furthermore, the continued evolution of global compliance frameworks, such as NIS2 in Europe, suggests that businesses will need to maintain agility and continuous monitoring of international regulatory landscapes to ensure ongoing adherence and sustained market access.
Beyond the Headlines
The rise of sovereign compliance frameworks reflects a deeper global trend towards data localization and national digital sovereignty, driven by concerns over cybersecurity, data privacy, and national security. For U.S. companies, this trend implies a shift from a 'one-size-fits-all' approach to a more nuanced, country-specific compliance strategy. It highlights the ethical dimension of data governance, where nations are asserting greater control over how data generated within their borders is handled, stored, and protected. This could lead to increased operational costs for multinational corporations, as they may need to establish localized data centers or adapt their IT infrastructure to meet diverse national requirements. The long-term implication is a more fragmented global digital landscape, potentially challenging the free flow of data and necessitating innovative solutions for maintaining global interoperability while respecting national sovereignty.