
What's Happening?
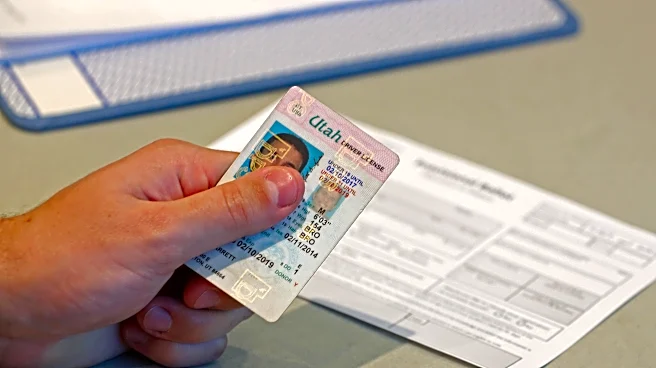
A data breach at Fireworks AI has exposed the license records of 150,000 Uber drivers, according to a report by IANS. This updated figure significantly increases the scope of the incident, which also involved Notion chat transcripts and a Cursor credential.
The breach underscores the hidden risks within the AI supply chain, where data can travel through multiple providers without direct user knowledge. Many customers whose data was compromised may not have directly interacted with Fireworks AI but used tools that relied on its services. The incident reveals that the breach continued to expand even after initial warnings, with the number of exposed driver license records jumping from thousands to 150,000. This situation raises critical questions for Uber regarding the security of data that passed through a vendor chain unknown to its drivers.
Why It's Important?
This incident is important because it exposes the vulnerabilities inherent in the complex AI supply chain, where data can be indirectly exposed through third-party tools. For U.S. industries, particularly those relying on AI services, this breach serves as a stark warning about the need for rigorous vendor assessment and data governance. Uber drivers, whose personal information has been compromised, face increased risks of identity theft and other malicious activities. Companies that utilize AI tools are now compelled to scrutinize their vendors' data handling practices, including subprocessors, data retention policies, and incident response capabilities. The breach highlights that even seemingly innocuous chat tools or coding assistants can transmit sensitive data to underlying AI providers, making it crucial for businesses to understand the full data flow within their technological ecosystems. The incident also emphasizes the need for robust security measures, such as replacing static keys with short-lived credentials and implementing secret scanning with redaction for prompts.
What's Next?
Companies that relied on Fireworks AI through other tools are now advised to identify which vendors used the service, review the data entered into those tools by staff, and rotate any potentially compromised credentials. IANS recommends that firms ask every software vendor with an AI feature about their subprocessors, data usage, retention policies, and breach notification protocols. Providers are expected to demonstrate how they enforce data retention across inference, analytics, and development work, including temporary copies. Incident response plans must be updated to cover downstream exposure, requiring teams to identify affected conversations, review them for credentials, and rotate any secrets found. The focus will be on obtaining audit evidence from providers to guide cleanup efforts. The long-term implication is a push for greater transparency and accountability in the AI supply chain to rebuild trust among users and businesses.
Beyond the Headlines
The Fireworks AI breach extends beyond a typical data compromise, revealing deeper implications for data privacy and the ethical use of AI. The incident highlights a critical blind spot where end-users and even direct customers are unaware of the full chain of data processing and storage. This lack of transparency can lead to significant legal and ethical challenges, as companies may be held responsible for breaches occurring at third-party vendors they indirectly engage. The exposure of Notion chat transcripts and Cursor credentials underscores the sensitivity of everyday digital interactions and development workflows, suggesting that even seemingly benign data can become a vector for large-scale compromise. This event could trigger a re-evaluation of data governance frameworks, pushing for stricter regulations and industry standards that mandate transparency and robust security across the entire AI supply chain, ultimately shaping how businesses and individuals interact with AI-powered services.