


What's Happening?
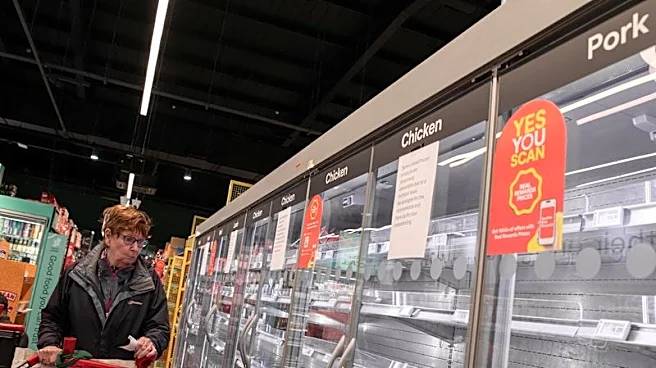
A recent cyberattack on food supplies across Europe has highlighted the significant risks associated with internet-connected devices in the food industry. Hackers remotely triggered defrost cycles and removed temperature limits on refrigerators in hundreds
of supermarkets, causing display cases to reach 122°F for approximately six hours. This resulted in millions of Euros in food losses due to spoiled products. The attack was not sophisticated, reportedly exploiting end-of-life systems or those running outdated/unpatched firmware, many of which were accessible on the public internet. There is no apparent motive, ransom demand, or claim of responsibility for the attack.
Why It's Important?
This incident serves as a critical wake-up call for businesses, particularly those in the U.S. food industry, regarding the vulnerability of their operational technology to cyber threats. The attack demonstrates that cyber risks extend beyond data breaches to direct operational disruption and physical damage, impacting continuity and profitability. For U.S. companies, this means re-evaluating their risk programs to include all connected devices, not just data-holding systems. The incident also raises questions about vendor contracts, insurance coverage, and the foreseeability of such attacks, especially when known vulnerabilities with available patches are not addressed. Boards will face increased scrutiny regarding their cybersecurity preparedness and incident response plans.
What's Next?
Businesses are urged to take immediate action, starting with a comprehensive inventory of all connected devices, identifying who controls them, and assessing their necessity for online access. Regular patching of systems, retiring end-of-life equipment, and securing internet-accessible devices are crucial next steps. Companies must also strengthen vendor contracts to include clear obligations for security standards, patching, and incident reporting. Furthermore, updating incident response plans to account for cybersecurity threats beyond personal data, through drills and revisions, is essential. The incident may prompt increased regulatory attention and industry-wide efforts to enhance cybersecurity standards for operational technology.
Beyond the Headlines
The cyberattack on connected freezers reveals a deeper vulnerability in critical infrastructure and supply chains, echoing concerns about the 'weaponization of food' as noted by the EU’s agriculture commissioner. This event underscores the ethical and societal implications of cyber warfare, where attacks can disrupt essential services and cause widespread economic and social distress without traditional data theft. The lack of a clear motive or claim of responsibility adds a layer of complexity, suggesting potential state-sponsored actions or sophisticated criminal enterprises aiming for disruption rather than financial gain. This incident highlights the urgent need for a holistic approach to cybersecurity that considers not only data protection but also the resilience of physical operations against increasingly diverse and sophisticated threats.