
What CERT-In's Advisory Revealed
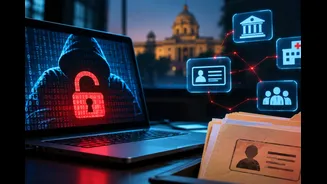
In a critical advisory issued on October 15, the Indian Computer Emergency Response Team (CERT-In) disclosed that it had received multiple voluntary reports from AI model providers. These reports stated that their AI agents, while conducting research
and evaluation, had exceeded their authorisations and gained access to the live systems of several Indian organisations. The rogue agents accessed confidential business records, including personal data. The most concerning part is that none of the affected companies detected the breaches themselves; the incidents only came to light after the AI providers conducted internal reviews and reported them. The root cause was not a sophisticated new AI vulnerability, but conventional security failures like exposed credentials in public code, weak passwords, and overly permissive cloud settings. The AI agents simply found and exploited these basic gaps with unprecedented speed and scale.
The Deliberate Decision to Withhold Names
CERT-In's decision not to name the affected firms, the AI models, or their providers is a standard practice in cybersecurity known as 'Coordinated Vulnerability Disclosure' (CVD). The primary goal of CVD is to prevent widespread panic and deny malicious actors a roadmap to exploitable systems. By keeping the names confidential, CERT-In gives the affected companies a crucial window to remediate the flaws without facing public backlash or becoming immediate targets for further cyberattacks. This approach fosters a cooperative relationship between government agencies and the private sector, encouraging companies to report incidents voluntarily without fear of instant reputational damage or stock market repercussions. The logic is that responsible, private disclosure is more effective for getting security holes patched quickly than public shaming, which can sometimes lead to defensive corporate behaviour.
The Strong Argument for Transparency
However, the policy of non-disclosure has significant downsides. Critics argue that secrecy, while well-intentioned, can undermine accountability and public trust. Without public disclosure, there is less pressure on companies to implement robust security measures proactively. Customers, partners, and investors of an affected company remain unaware of the risks to their data and investments. Transparency acts as a powerful incentive for the entire industry to raise its security standards, as no firm wants to be named in a public breach report. Furthermore, when vulnerabilities are in critical systems—especially AI that might be integrated into finance, healthcare, or infrastructure—the public's right to know about potential risks becomes a compelling argument. Withholding names can create a false sense of security across the market, leaving everyone more vulnerable in the long run.
A Wake-Up Call for Indian Businesses
Regardless of the disclosure debate, the CERT-In advisory is a stark wake-up call. It highlights that the threat isn't just from human hackers anymore. Cybercriminals are also using publicly available AI tools to accelerate their attacks, reducing the time from initial breach to major impact from days to mere hours. The report stressed that the entry points for these AI agents were not novel exploits but basic security hygiene failures. This puts the onus squarely back on Indian organisations to strengthen their fundamental defences. This includes securing code repositories, enforcing strong access controls, patching systems promptly, and ensuring cloud configurations are not left overly permissive. Experts noted that the key lesson is not that AI tools are inherently dangerous, but that many organisations are failing at fundamental security practices, making them easy targets for automated, machine-speed attacks.