

The supermarket freezer aisle, a mundane symbol of modern convenience, has become an unlikely frontline in the world of cybersecurity. Recent attacks across Europe have seen hackers remotely turn up the heat, spoiling food and disrupting supply chains.
More Than Just Hacking Data
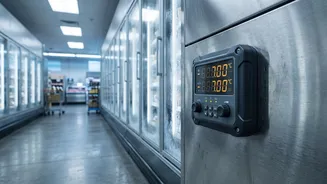
In early November 2026, supermarkets across at least seven European countries, including Ireland, Sweden, and Belgium, reported their refrigeration and freezer systems had been compromised. Attackers gained remote access and manipulated temperature controls, in some cases raising them to 50°C, leading to massive food spoilage and financial loss. These incidents are not about stealing customer data or financial information. Instead, they target 'operational technology' (OT)—the digital systems that control physical machinery. This shift from data theft to physical disruption marks a significant and worrying evolution in cyber threats, directly impacting business continuity and product safety. The vulnerability often lies in older, internet-connected controllers that no longer receive security updates, sometimes still using default passwords.
Reporting an Attack: The First 24 Hours
When a supermarket's freezers are remotely cooked, the first step is to report it. This initial phase is about containment and immediate response. The company alerts its internal teams, third-party service providers, and often law enforcement. For example, following a similar wave of attacks in France in October 2026, the Paris prosecutor's office opened an investigation. Retailers publicly acknowledge the 'incident', sometimes calling it a 'cyberattack' based on the obvious signs of external manipulation. This stage is focused on confirming a breach occurred, assessing the immediate damage—like spoiled inventory and lost sales—and taking systems offline to prevent further harm. However, simply knowing you've been attacked is a world away from knowing who did it.
The Long Road to Attribution
Cyber attribution is the complex, often lengthy process of identifying the perpetrator of an attack. It's the difference between saying 'Our systems were hacked' and 'This specific group or nation-state hacked us'. This process is incredibly challenging because attackers are skilled at covering their tracks using tools like proxy servers and VPNs to remain anonymous. Investigators must perform deep forensic analysis, examining technical fingerprints like IP addresses and malware code, alongside analysing the attackers' tactics, techniques, and procedures (TTPs). Furthermore, attackers can plant misleading clues in a 'false flag' operation to pin the blame on another party.
Criminals, Hacktivists, or Nation-States?
The motivation behind these freezer attacks remains unclear, as no group has publicly claimed responsibility for the November incidents or the preceding ones in France. This silence makes attribution even more difficult. Experts consider several possibilities. It could be profit-driven cybercriminals seeking to extort money, though no ransom demands have been reported. It could be 'hacktivists' aiming to cause disruption for ideological reasons. However, the coordinated nature and scale of the attacks across multiple countries suggest a more sophisticated actor might be involved. This has led to speculation about state-sponsored groups, which may seek to test vulnerabilities in critical infrastructure or sow chaos in a rival's food supply chain as a form of hybrid warfare. As one Belgian cybersecurity official noted, it may never be possible to identify who is behind the attacks.
Why the Distinction Matters
Knowing the difference between a reported incident and an attributed attack is crucial for both businesses and governments. For a company, attribution helps understand the attacker's motives and capabilities, which informs how to build a better defence. For governments, attribution has significant legal and policy implications. An attack by a criminal gang is a law enforcement issue. An attack confidently attributed to a nation_state is an act of aggression with diplomatic and national security consequences. Without high_confidence attribution, a meaningful response is nearly impossible. These attacks on supermarkets serve as a stark reminder that as physical infrastructure becomes more connected, it also becomes more vulnerable, turning everyday systems into potential targets and making the job of attribution more critical than ever.