
A Coordinated Thaw
In recent weeks, a wave of disruptive cyberattacks has targeted supermarket chains across at least nine European countries, including France, Belgium, Sweden, Ireland, and Italy. The method is chillingly simple yet devastatingly effective: hackers gain
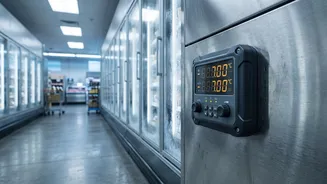
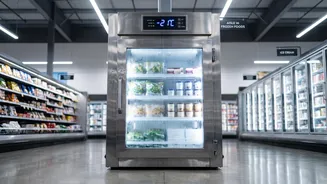
remote access to the digital controllers of refrigeration and freezer units, forcing them into defrost mode or raising their temperatures to as much as 50°C. The result is catastrophic food spoilage, with individual stores reporting losses of over €130,000 and the total damage running into millions. These are not attacks on corporate IT systems to steal data; they are targeted assaults on operational technology (OT)—the hardware and software that control physical machinery in the real world.
The Vulnerability in Our Food Chain
The attackers have exploited a critical weakness in modern infrastructure: the Internet of Things (IoT). Many of the targeted refrigeration controllers are older, internet-connected models that no longer receive security updates. These devices, sometimes with weak or default passwords and exposed directly to the internet without adequate firewalls, become low-hanging fruit for malicious actors. Cybersecurity experts warn that while retailers have focused on protecting customer data and payment systems, the operational equipment that ensures business continuity has often been overlooked. The attacks serve as a stark reminder that the food supply chain, a piece of critical national infrastructure, is only as strong as its most vulnerable digital link.
The Technical Challenge of Attribution
Despite multiple law enforcement agencies launching investigations, no attacker—be it a criminal gang or a state-sponsored group—has been publicly named. One major reason is the immense technical difficulty of cyber attribution. Attackers are masters of misdirection, routing their assaults through a labyrinth of compromised computers, proxy servers, and virtual private networks (VPNs) across multiple countries. This creates a digital hall of mirrors designed to obscure their true origin. Pinpointing the source of an attack with the high degree of certainty required for a public accusation is a painstaking process. As one official from the Centre for Cybersecurity Belgium noted, it's possible the culprits may never be identified.
The Politics of Silence
Beyond the technical hurdles, there are compelling strategic reasons why governments often remain silent even if they have strong suspicions. Publicly attributing a major cyberattack to another nation_state is a significant diplomatic act. If the evidence isn't ironclad, the accusation can be easily denied, making the accuser look weak or foolish. Furthermore, revealing what you know can compromise sensitive intelligence sources and methods, tipping off adversaries about your surveillance capabilities. In a geopolitical climate rife with tension, a government might choose to respond through quieter, non_public channels to avoid escalating a conflict, especially when the attack, while disruptive, has not resulted in loss of life.
Disruption as the Primary Goal
Notably, these attacks have not been accompanied by ransom demands, which typically characterize criminal ransomware operations. This has led many experts to believe the motive is not financial gain but disruption itself. The goal may be to sow chaos, test vulnerabilities, and undermine public confidence in the stability of the food supply chain. Some analysts speculate that state_sponsored actors could be behind the incidents, using them as a form of 'hybrid warfare' to destabilize rivals without firing a single shot. By targeting everyday infrastructure, attackers demonstrate their ability to cause widespread, tangible harm to civilian life, creating a powerful psychological impact.