

The Core Conflict: Control vs. Capability
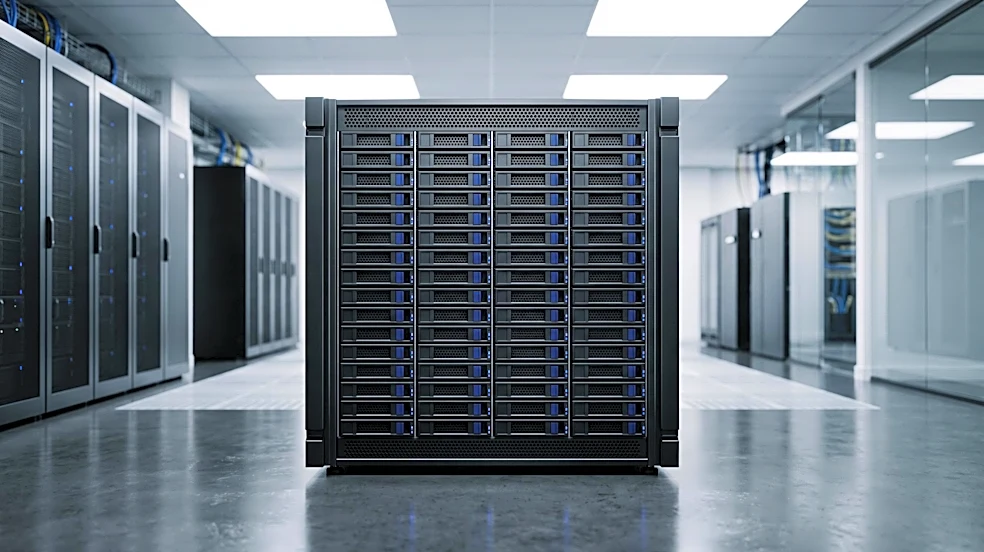
At the heart of the disagreement is a fundamental trade-off. One camp of security engineers argues that nothing is more secure than what you can physically touch. They champion on-premise data centers, where the firm owns the servers, manages the network,
and has complete control over who can access the hardware. For an accounting firm, this means knowing client financial records are locked within their own four walls, isolated from the multi-tenant environments of the public cloud. The other camp counters that this control is an illusion. They argue that top-tier cloud providers like Amazon Web Services (AWS) or Microsoft Azure have security budgets and engineering talent that dwarf what any single accounting firm can afford. These hyperscale providers offer advanced, automated threat detection and round-the-clock monitoring that are simply out of reach for most in-house IT teams. For them, the greater capability of the cloud outweighs the perceived safety of physical control.
The 'Shared Responsibility' Sticking Point
The debate intensifies around the cloud's 'Shared Responsibility Model'. In this framework, the cloud provider is responsible for the security of the cloud (the infrastructure, hardware, and core networking), while the customer is responsible for security in the cloud. This customer portion includes managing user access, encrypting data, and correctly configuring services. Pro-cloud engineers see this as a smart division of labor. However, skeptical engineers see it as a massive vulnerability. They argue that most data breaches in the cloud aren't due to the provider getting hacked, but due to customer misconfiguration. For an accounting firm, a single mistake—like leaving a storage bucket of client tax returns public—can be catastrophic. The disagreement boils down to trust: can a firm's IT staff master the complexities of cloud configuration and uphold their end of the security bargain?
The Compliance and Data Sovereignty Puzzle
Accounting firms operate under a thicket of regulations like Sarbanes-Oxley (SOX) and industry standards like PCI DSS, which govern how financial and personal data is handled. Engineers who favor on-premise solutions argue it's simpler to prove compliance when you can point to a specific server rack in your building. Data sovereignty—rules requiring citizen data to remain within a country's borders—is easier to manage when you control the physical location of the data. Conversely, cloud proponents argue that major providers offer robust compliance certifications for a wide range of regulations, saving firms the immense effort of building and documenting it themselves. They contend that navigating the global data regions offered by cloud providers is a manageable task, and the providers’ built-in tools for logging and auditing can actually make demonstrating compliance easier than with legacy on-premise systems.
Two Different Bets on a Human Problem
Ultimately, the disagreement is not just about machines, but about people. One side bets that it's safer to rely on a small, trusted internal team to manage a contained, on-premise environment. They worry about the shortage of skilled cloud security professionals and the constant risk of human error in a complex, code-driven cloud environment. The other side makes the opposite bet. They argue that finding, training, and retaining talent to manage aging on-premise hardware and bespoke security systems is the real challenge. They believe it's more strategic to leverage the world-class expertise embedded into cloud platforms and focus their limited internal resources on securing the applications and data that live on top. They're not outsourcing responsibility, but strategically partnering with a specialist.