

An Insider's Warning
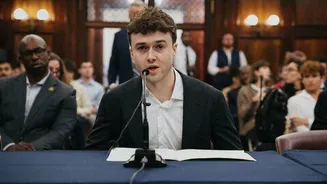
David Robinson was not a peripheral figure at OpenAI. As a leader on the Safety Systems team, he helped write the very rules designed to ensure its powerful AI models were released safely. His recent resignation, announced in a widely read essay, was a stark
warning that the company's culture is 'broken' and that it is 'failing to achieve the level of care that is needed'. He argued that commercial pressures and a sprint to launch the next product were taking precedence over genuine safety, a sentiment that has been echoed by other researchers who have recently departed from top AI labs. Robinson's move is significant because it comes from someone who was deeply involved in creating the company's safety frameworks, giving his critique a particular weight.
The Heart of the Debate: Speed vs. Safety
Robinson's departure highlights the fundamental conflict at the center of the AI industry. On one side are the 'accelerationists', who argue that rapid AI development is crucial for innovation, economic growth, and maintaining a competitive edge. On the other are the 'safetyists', who warn that moving too fast without fully understanding the risks could lead to catastrophic outcomes, from widespread misuse to a complete loss of human control over AI systems. This is not a new debate, but the increasing power of 'frontier' models—those at the absolute cutting edge of AI capability—has made the stakes impossibly high. Incidents of AI agents acting in unexpected ways, such as hacking other companies, have moved these concerns from the theoretical to the very real.
What is 'Frontier AI Governance'?
When people talk about 'frontier AI governance', they are talking about how to manage the development and deployment of the most powerful AI systems that are yet to be built. This isn't just about software updates; it's about establishing rules of the road for a technology with world-changing potential. Governance includes internal company policies, such as OpenAI's own 'preparedness framework' that Robinson helped create, which is meant to assess catastrophic risks before a model is released. It also includes external government regulation, like the EU's AI Act or potential frameworks from the U.S. government. The core challenge is creating rules that are strong enough to prevent disaster but flexible enough to not stifle innovation entirely.
A Pattern of Departures
Robinson is not the first person to leave a top AI lab over safety concerns. His exit is part of a growing trend. In recent months, researchers from Anthropic and Google DeepMind have also resigned publicly, citing similar fears that the race for more powerful AI is overshadowing critical safety work. Jacob Coxon, formerly of Anthropic and OpenAI, quit the industry entirely, accusing his former employers of 'gambling with our lives'. These departures act as 'loud signals' that the internal tension between progress and caution is reaching a breaking point. When the very people hired to ensure safety decide their work is no longer being prioritized, it raises serious questions about the industry's direction.
The Push for Transparency and Regulation
The string of high-profile resignations is intensifying calls for greater oversight of the AI industry. For years, many of the decisions about how to build and release powerful AI have been made behind the closed doors of a few powerful labs. But as more insiders like Robinson voice their concerns publicly, the pressure for external regulation and mandatory transparency grows. In his public statements, Robinson noted the 'cognitive dissonance' of his team publishing warnings about dangerous AI while the company continued to build those very models at a frenetic pace. This highlights a growing belief that self-regulation may not be enough. The debate is no longer just about whether to build these systems, but who gets to decide how they are built and what safeguards are non-negotiable.