India’s cybersecurity agency CERT-In has issued a critical warning about two newly discovered flaws in PHP, the programming language that runs a large share of the world’s websites. The bugs, nicknamed “PHP2Shell”, have already pushed government websites in several countries offline as a precaution, and security researchers say attackers are actively trying to exploit them.
CERT-In published its vulnerability note, CIVN-2026-0510, on October 21, the same day PHP released fixes. The US National Security Agency has also flagged the risk.
What Is PHP2Shell?
PHP2Shell is the name given to two flaws, tracked as CVE-2026-109618 and CVE-2026-109619. According to CERT-In, they could let a remote attacker run any code they want on a web server, which can lead to a complete
takeover of the system. The European Union’s cybersecurity team CERT-EU rates them 9.2 out of 10 for severity.
The flaws are serious because attackers don’t need a password. PHP’s developers say the risk is highest on servers that use a common setup called mod_php, where a single request can trigger the attack before the website’s own code even runs.
PHP powers WordPress, Drupal, Joomla and Magento, along with a large number of shopping sites, blogs, college portals and small business websites. That is why the warning has spread so fast.
Which Websites Have Gone Offline?
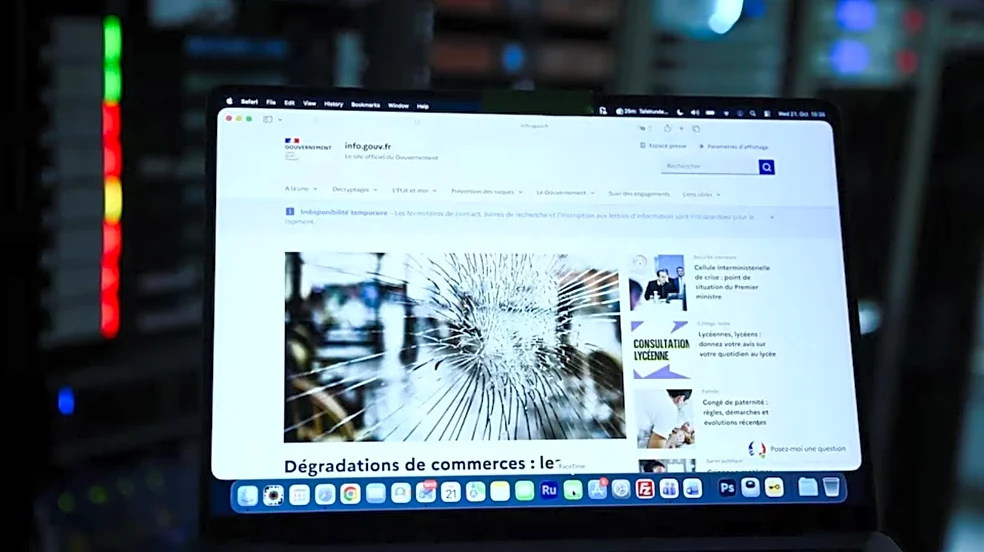
Finland temporarily shut its government’s public web services. In the Netherlands, websites of the cybersecurity agency, a public health agency and the lower house of parliament became inaccessible. The Wikimedia Foundation took some systems offline as a precaution, making parts of Wikipedia unreachable for a while, according to reports.
No Indian websites have been reported offline so far.
What Does This Mean For You?
If you only browse the internet, you can’t patch this flaw yourself. The fix has to come from the companies and people who run websites. Still, a hacked website can leak user data or be used to spread scams, so be careful over the next few days. Don’t enter card details on websites you don’t trust, ignore unexpected “update your password” emails, and use different passwords on different sites.
What Should Website Owners Do?
CERT-In has asked users to install the patched versions: PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35. If you use WordPress or a hosting company, check with your hosting provider that the update has been applied. PHP 8.1 and older versions no longer get official fixes.
If a server can’t be updated right away, the UK’s National Cyber Security Centre recommends taking it offline until it can be.