

What's Happening?
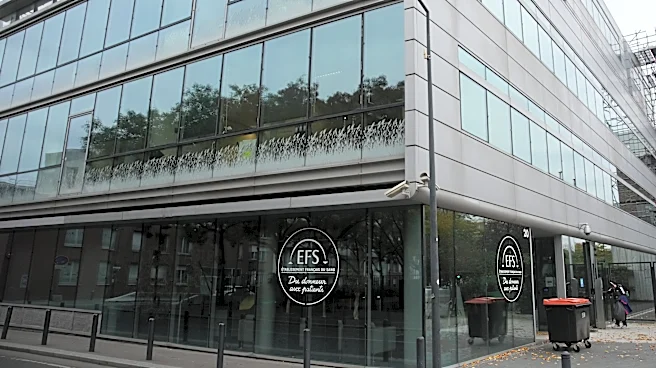
Critical infrastructure, specifically refrigeration equipment, has been targeted in a series of cyberattacks across Europe and on U.S. military bases. In France, three sites handling blood and plasma bags experienced incidents where cold rooms were raised
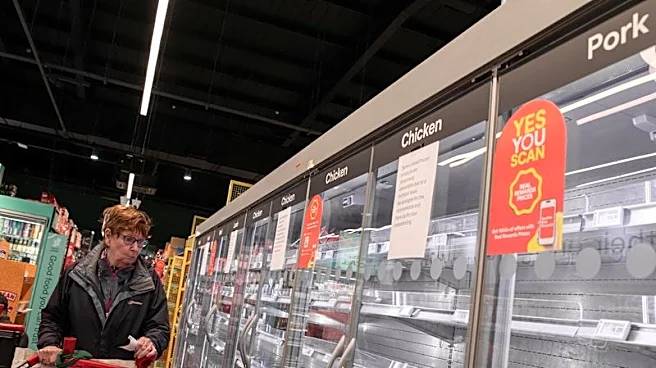
to high temperatures, though fail-safe measures prevented damage to samples. Widespread attacks also affected supermarket chains in at least 11 European countries, leading to significant food spoilage. Similar incidents occurred in October in France and in August on six commissaries and grocery stores on U.S. military bases, resulting in spoiled food. The Pentagon is investigating these incidents in collaboration with French law enforcement. Many of these hacks exploit vulnerabilities in temperature controllers, particularly those made by the Danish firm Danfoss, often due to outdated firmware and weak, unpatched systems exposed to the internet.
Why It's Important?
These attacks underscore a critical vulnerability in the U.S. and global infrastructure: the cybersecurity of Internet-of-Things (IoT) devices. The compromise of refrigeration systems, especially those storing vital medical supplies like blood and plasma, poses a direct threat to public health and safety. For the U.S. military, attacks on commissaries and grocery stores not only result in financial losses from spoiled food but also highlight potential weaknesses in the supply chain and operational readiness. The ease with which these systems are being exploited, often due to basic cybersecurity failures like outdated software and weak passwords, indicates a widespread lack of fundamental digital defense practices. This situation could lead to significant economic disruption, public health crises, and national security concerns if more critical systems are targeted and compromised.
What's Next?
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an alert, urging customers to update products and address vulnerabilities such as authentication bypasses, arbitrary code injections, and weak configurations in cold storage systems. The ongoing investigations by the Pentagon and French law enforcement aim to identify the perpetrators and determine if the attacks are connected. This series of incidents serves as a wake-up call for organizations to prioritize cybersecurity fundamentals, particularly for IoT devices connected to critical infrastructure. Expect increased scrutiny and potential regulatory actions regarding the security of such devices, along with a push for better patch management and stronger authentication protocols to prevent future attacks.
Beyond the Headlines
The 'fridge-hacking spree' reveals a deeper issue beyond immediate cyber threats: the growing dependence on interconnected technology without adequate protective measures. This trend, where convenience often outweighs security considerations, leaves essential services vulnerable to both accidental failures and malicious actors. The incidents highlight the 'security through obscurity' fallacy, where the perceived unimportance of certain devices leads to neglect, making them easy targets. This situation calls for a cultural shift in how technology is integrated into critical systems, emphasizing security by design and continuous monitoring. The long-term implications include the need for robust international cooperation in cybersecurity, as attacks can originate anywhere and impact global supply chains and public services, necessitating a unified approach to digital defense.