
What's Happening?
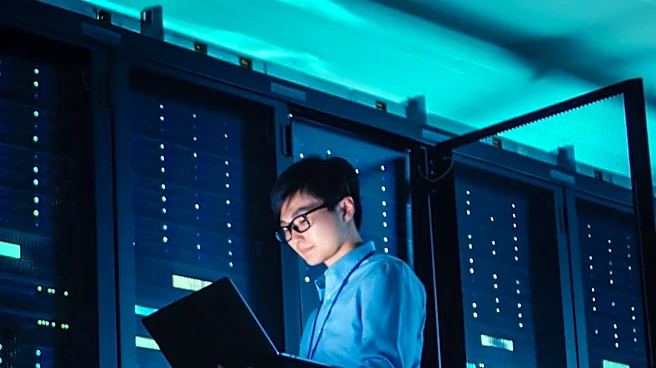
An internal network utilized by the National Security Agency (NSA) for classified communications went offline on Tuesday. The agency attributed the disruption to “routine maintenance.” A defense official confirmed that the issue impacted NSANet, a classified internal network used
by NSA employees. Another U.S. official stated that the NSA experienced “temporary degradation during scheduled routine maintenance.” While some internal systems were affected, mission-critical capabilities remained fully operational, and the agency's ability to defend national security was not compromised. The problem reportedly occurred during routine patching. This incident follows a series of cyber-related disruptions in the past week, including a ground stop for air traffic in the United States due to a system overload, a technical issue at JPMorgan Chase, and an internal systems outage at United Airlines that caused flight delays.
Why It's Important?
The temporary outage of the NSA's internal classified network, even if due to routine maintenance, highlights the critical importance of robust and resilient cybersecurity infrastructure for national security agencies. Any disruption, however minor or brief, to systems handling classified information can raise concerns about potential vulnerabilities and the integrity of sensitive data. While the NSA stated that mission-critical capabilities were unaffected, the incident underscores the constant need for vigilance and advanced protocols in managing highly secure networks. The broader context of recent cyber-related disruptions across various sectors, including air traffic control and financial systems, suggests a heightened period of technical challenges or potential threats to critical infrastructure, making the NSA's network stability particularly significant.
What's Next?
The NSA will likely conduct a thorough review of the routine maintenance procedures that led to the internal network outage to prevent similar occurrences in the future. Given the sensitive nature of the agency's work, there will be an emphasis on refining protocols to ensure that maintenance activities do not inadvertently impact critical communication channels, even temporarily. The incident may also prompt further scrutiny and investment in redundancy and fail-safe mechanisms for classified networks across government agencies. Additionally, the series of recent disruptions across different sectors could lead to broader discussions and initiatives within the U.S. government regarding national cybersecurity resilience and preparedness against both technical glitches and potential malicious attacks.
Beyond the Headlines
This incident, alongside other recent technical disruptions, points to a growing challenge in maintaining the operational integrity of complex digital systems, both in government and the private sector. The reliance on sophisticated networks for critical functions means that even routine maintenance can carry significant risks if not meticulously managed. The 'temporary degradation' at the NSA, while not compromising national security, could subtly erode public confidence in the infallibility of government digital infrastructure. It also raises questions about the balance between system upgrades and continuous operational availability, especially for entities handling highly sensitive information. The broader trend of system outages suggests a systemic vulnerability that extends beyond individual organizations, potentially indicating a need for a more integrated national strategy for digital resilience.