
What's Happening?
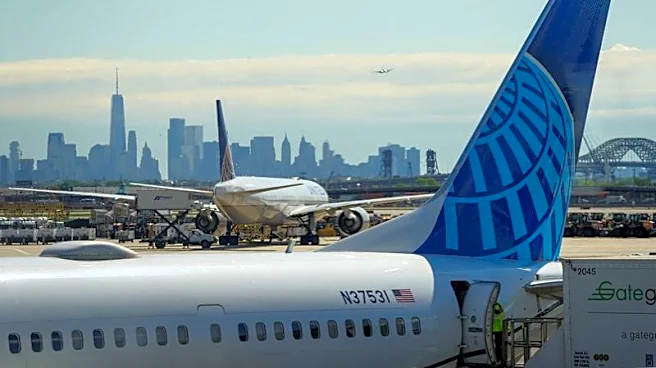
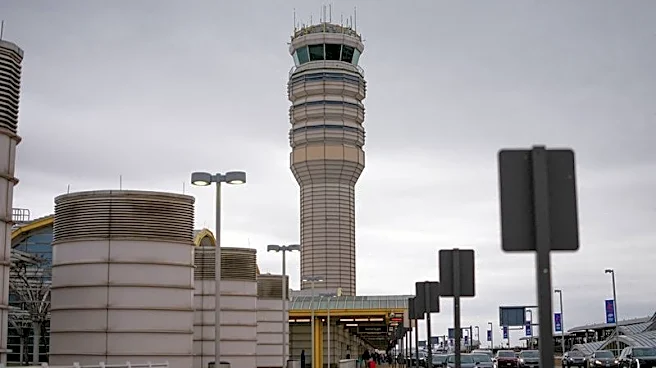
The U.S. Government Accountability Office (GAO) has issued a warning regarding significant cybersecurity vulnerabilities within the Federal Aviation Administration's (FAA) air traffic control systems. The report indicates that malicious actors could exploit
weaknesses in authentication, encryption, and protocol design of systems like the Aircraft Communications Addressing and Reporting System (ACARS) and Controller-Pilot Data Link Communications (CPDLC). These vulnerabilities could allow for the transmission of fraudulent messages, including fake clearance cancellations, potentially leading to flight delays or safety issues. The GAO found that the FAA lacks comprehensive real-time threat monitoring and has not completed necessary risk assessments and security documentation for several spectrum-dependent systems. The FAA concurred with all nine recommendations made by the GAO, which include strengthening authentication and data protection, conducting spectrum risk assessments, and improving interagency collaboration.
Why It's Important?
The GAO's findings highlight a critical national security and public safety concern. The potential for malicious actors to spoof air traffic control messages could have catastrophic consequences, ranging from widespread flight disruptions and economic losses to severe aviation accidents. The reliance on digital communication systems in modern air travel makes these vulnerabilities particularly dangerous. The report underscores the urgent need for robust cybersecurity measures within critical infrastructure sectors. The FAA's acknowledgment of the recommendations is a positive step, but the ongoing nature of these vulnerabilities means that millions of air travelers and the entire U.S. aviation industry remain at risk until these issues are fully addressed. This situation also emphasizes the broader challenge of securing complex, interconnected systems against evolving cyber threats.
What's Next?
The FAA is expected to implement the nine recommendations provided by the GAO to enhance the security of its air traffic control systems. This will involve working with federal agencies and aviation industry stakeholders to develop and execute a plan for strengthening authentication and data protection, specifically targeting spoofing, unauthorized transmissions, and message tampering. The FAA will also need to complete formal risk assessments for its spectrum-dependent systems and establish a capability for continuous, real-time monitoring of spectrum-related threats. The progress on these recommendations will likely be subject to ongoing oversight by the GAO. The aviation industry, both domestically and internationally, may also review and strengthen its own cybersecurity protocols in light of these warnings.
Beyond the Headlines
Beyond the immediate safety concerns, the GAO's report on FAA cybersecurity vulnerabilities points to a broader systemic challenge in protecting critical national infrastructure from sophisticated cyber threats. The identified weaknesses in authentication and encryption are not unique to aviation and could be indicative of similar vulnerabilities in other essential sectors. This situation underscores the continuous arms race between cybersecurity defenders and malicious actors, requiring constant vigilance, investment, and adaptation. The report also highlights the importance of interagency collaboration and information sharing in addressing complex cyber threats that transcend individual agency boundaries. The long-term implications could include a re-evaluation of how federal agencies prioritize and fund cybersecurity initiatives, potentially leading to more stringent regulations and increased accountability for securing vital public services.