

What's Happening?
The Federal Bureau of Investigation (FBI) has issued a warning regarding a sophisticated North Korean cyber operation dubbed 'FaceStealer.' This operation has reportedly stolen over $400 million in cryptocurrency within 18 months and amassed more than
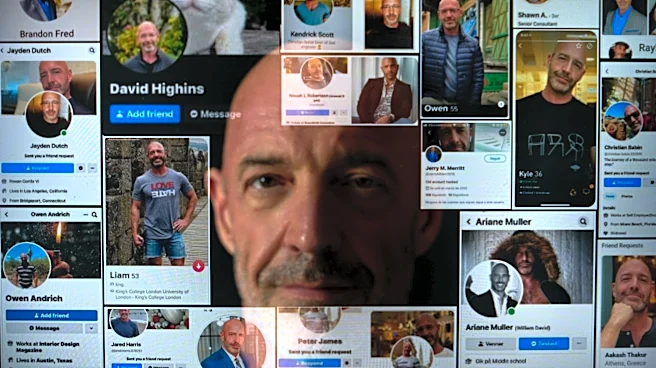
900 webcam recordings of victims. The hackers use these recordings, along with hijacked communication accounts and AI-generated videos, to impersonate individuals in counterfeit video meetings. They invite targets to what appear to be legitimate Zoom or Microsoft Teams meetings, often referencing established business relationships. During these fake meetings, attackers create a fabricated technical issue, prompting victims to install malware under the guise of a solution. This malware then harvests credentials, records keystrokes, captures screens, and establishes persistent access. The FBI notes that the operation has expanded to target maintainers of widely distributed open-source software, posing a significant supply-chain threat. The Department of Justice recently announced the seizure of cloud infrastructure supporting this operation.
Why It's Important?
The 'FaceStealer' operation highlights a critical evolution in cybercrime, moving beyond traditional phishing to weaponize authentic human identities and AI-generated content. The use of real webcam recordings and deepfakes makes these attacks exceptionally convincing, undermining trust in digital communications and professional interactions. The targeting of open-source software maintainers is particularly concerning, as a compromise in this area can lead to widespread distribution of malicious software through legitimate channels, affecting numerous organizations and individuals far removed from the initial targets. The substantial financial losses, exceeding $400 million, underscore the economic impact of such sophisticated fraud schemes. This development also raises significant questions about the efficacy of current digital verification methods and the need for enhanced cybersecurity protocols in both corporate and individual settings.
What's Next?
Following the seizure of cloud infrastructure by the Department of Justice, investigations will likely continue to assess the full extent of the 'FaceStealer' operation and identify additional victims. Cybersecurity firms and law enforcement agencies will likely intensify efforts to track and disrupt similar state-sponsored cyber activities. Organizations and individuals are expected to receive increased advisories on how to identify and protect themselves from advanced impersonation techniques, including deepfakes and manipulated video calls. There may be a push for improved authentication methods and greater scrutiny of software supply chains to prevent the infiltration of malicious code. The incident could also prompt further collaboration between international law enforcement agencies to combat cross-border cybercrime and hold state-sponsored actors accountable.
Beyond the Headlines
This operation exposes a deeper vulnerability in the digital age: the reliance on visual and auditory cues for trust in online interactions. As AI technology advances, the ability to generate convincing synthetic media will make it increasingly difficult to distinguish between genuine and fabricated digital identities. This raises profound ethical and legal questions about digital identity verification, consent for data usage, and the potential for widespread misinformation and fraud. The 'FaceStealer' method, which reuses stolen faces for subsequent attacks, creates a self-perpetuating cycle of compromise, turning victims into unwitting tools for future crimes. This necessitates a re-evaluation of how digital trust is established and maintained, potentially leading to the development of more robust, multi-factor authentication systems that go beyond visual confirmation.